When a compromised administrator does not mean a compromised identity
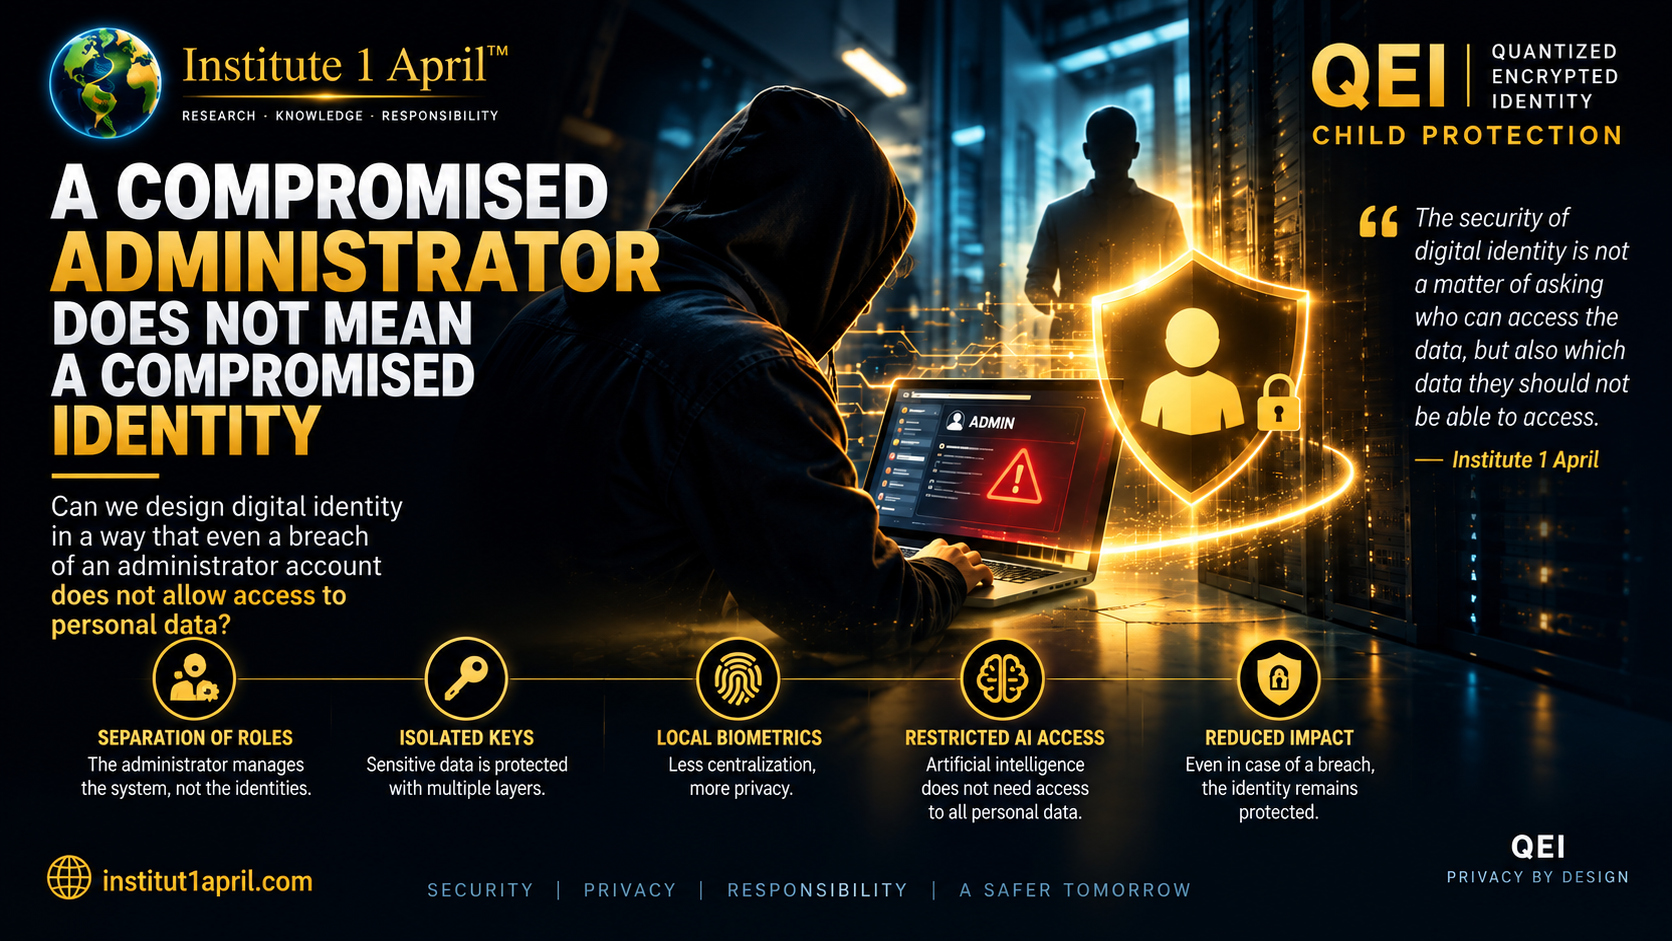
Can digital identity be designed so that even a breach of an administrator account does not grant direct access to users’ personal data?
Digital identity is becoming one of the essential foundations of modern society. We use it to access healthcare, bank accounts, public administration, electronic business services and many other services.
Yet as digital systems develop, a question arises that we often overlook: what happens when an attacker targets not the user, but the person or system responsible for managing their data?
Even a carefully protected user account can become vulnerable if an attacker obtains privileged access, administrative credentials or control over infrastructure that stores sensitive information.
Advances in artificial intelligence add another dimension to this problem. Attackers can automate stages of an attack, analyse large volumes of stolen data and identify links between those records more quickly.
We therefore need to ask whether the future of digital identity can truly rest solely on ever-stronger protection of access to data.
What if systems were designed so that compromising an administrator account would not, by itself, be enough to reveal an individual’s identity?
When the administrator becomes a weak point
In many information systems, administrators have extensive privileges to maintain infrastructure, troubleshoot problems and keep services running.
Such privileges are often necessary, but they can also create a significant security risk.
Consider a healthcare institution holding the personal records of tens of thousands of patients.
If an attacker gains privileged access to its information systems, they may, depending on the architecture and security controls in place, attempt to access databases, alter records or obtain other sensitive information.
The problem is not necessarily that an individual user has been careless.
It can arise from the very design of a system that concentrates too much data, too many privileges or too many ways of linking information in one place.
This is why contemporary cybersecurity increasingly emphasises the principle of least privilege and a Zero Trust architecture.
Even these approaches, however, cannot eliminate every risk.
Can an administrator run a system without knowing the user’s identity?
This question is one of the starting points for the QEI – Quantized Encrypted Identity concept being developed as a research initiative by Institute 1 April.
The central idea is not simply to add more protection to existing databases, but to explore a different architecture for digital identity.
In such an architecture, individual functions would be separated, sensitive data protected by different security mechanisms, and disclosure limited to procedures that are necessary and appropriately authorised.
An administrator could manage the infrastructure, monitor its technical health and resolve faults without automatically gaining the right to view a person’s complete identity.
This would establish a crucial distinction between the right to administer a system and the right to access personal data.
How could QEI limit the consequences of a breach?
The QEI development concept explores several interconnected security principles.
1. Separating identity from the verification process
Many digital services request more personal data to verify a particular attribute than they actually need.
For example, confirming that someone is an adult does not necessarily require a service provider to learn the person’s name, address or date of birth.
QEI therefore explores cryptographically protected credentials and digital tokens through which a person could prove an entitlement or an attribute without unnecessarily revealing their identity.
Tokenisation alone, however, does not guarantee anonymity. The architecture must also prevent unnecessary linking of personal information and identifiers across different services.
2. Separating security keys and privileges
If a system relies on a single privileged permission or a centrally accessible key to unlock all protected data, compromising that key or permission can have far-reaching consequences.
QEI envisages researching an architecture that separates critical security functions and may require several independent approvals for especially sensitive operations.
Such mechanisms could include multi-party or threshold authorisation, under which a single administrator would be unable to carry out certain high-risk operations alone.
This approach could reduce dependence on any one person, credential or component.
3. Local and isolated processing of biometric data
Biometric data calls for particular care.
A password can be changed. A fingerprint, face or another biometric characteristic cannot simply be replaced after misuse.
One proposed direction for QEI is therefore local or appropriately isolated verification of biometric characteristics wherever biometric verification is necessary.
The aim is to reduce the need to collect and transfer biometrics centrally and prevent their unauthorised use for other purposes.
Local processing is not a complete safeguard in itself. Security depends on the hardware, software implementation, storage method and protection against spoofed biometric inputs.
4. Restricting access within the system itself
An important goal is to prevent any single administrative role from enjoying unlimited access to all information.
Separation of duties, time-limited permissions, traceability of sensitive operations and independent oversight could help reduce the risk of insider abuse.
In a well-designed system, data access would be tied to a specific authorisation and a demonstrable need, rather than merely to a user’s place in the administrative hierarchy.
5. Revocation, recovery and incident response
No digital system can promise complete resilience against every possible attack.
The possibility of individual components being compromised therefore needs to be considered from the beginning of the design process.
QEI would need mechanisms to revoke compromised credentials, replace relevant security keys, temporarily restrict access and securely restore trust.
Crucially, a security incident in one part of the system should not automatically compromise every other connected identity.
Artificial intelligence: a new risk to trust in digital systems
Artificial intelligence can be valuable for detecting anomalies, identifying suspicious activity and responding more quickly to security incidents.
But attackers can also exploit the same technological capabilities.
AI can be used to create more convincing phishing messages, fabricate voices and images, and automate attempts to gain access.
If an attacker obtains a large collection of personal information, advanced analytical tools can help them link records and identify individuals.
This is where another proposed direction of QEI becomes important.
An AI system should not automatically gain access to personal data merely because it operates within an information system.
Its permissions and access should be limited to what is needed for the task it performs.
For instance, an AI system detecting suspicious logins would generally not need to see all of a user’s personal or biometric data.
Instead of accessing the person’s entire identity, it could process limited security signals and the information necessary to detect a potential threat.
This would not eliminate all risks, but it could reduce the amount of sensitive information exposed to possible misuse.
What would happen if an attacker gained administrator access?
Imagine a future system built around the security principles described above.
An attacker obtains administrative credentials and gains access to part of its infrastructure.
In a more traditionally designed system, this might enable access to extensive databases, depending on the safeguards in place.
In the proposed QEI architecture, however, the attacker could encounter a different situation.
Even with certain administrative rights, they would not necessarily possess the cryptographic keys, biometric information or other components needed to associate protected records with a person’s real identity.
Particularly sensitive procedures could require additional independent approvals.
The system might also detect unusual use of privileges, restrict further operations and activate incident-response procedures.
The result would depend on the actual technical implementation. An attacker who also controlled critical components, devices or recovery procedures might still bypass the protections.
The goal is not to promise that a breach could never occur, but to prevent a single breach from automatically exposing every identity.
From protecting data to reducing the consequences of compromise
For a long time, information security has been understood primarily as the prevention of unauthorised access.
Firewalls, passwords, multi-factor authentication and encryption remain essential.
But the future also demands that we consider how to prevent widespread harm when one security layer fails.
That calls for a different understanding of trust.
Users should not have to depend solely on whether a provider’s administrator is sufficiently cautious, whether an employee identifies a phishing attempt or whether a software component was patched in time.
Digital identity should be designed so that different layers of security limit the consequences of an error or abuse.
Such an architecture requires more than technology. It needs clear governance rules, independent security assessments, accountability among operators and effective rights for individuals.
QEI as a research initiative of Institute 1 April
Through the QEI concept, Institute 1 April is exploring ways to build digital identity systems in which the protection of personal data is not an added security feature, but a fundamental design principle.
Key objectives include minimising unnecessary disclosure, separating sensitive functions, restricting administrative privileges and developing identity-verification procedures without excessive centralisation of personal information.
QEI is a research and development concept, not a completed, independently tested or certified production system. The mechanisms discussed here are proposed research and architectural directions whose effectiveness would need to be demonstrated through implementation, security testing and independent evaluation.
That is precisely the purpose of this research: to examine whether the next generation of digital identity infrastructure can be designed differently.
Conclusion: identity must remain protected even when trust in an administrator fails
No information system is completely secure.
Yet there is a fundamental difference between a system in which one compromised account can lead to a mass data breach and one that limits this risk through several independent layers of protection.
The future of digital identity should therefore be about more than who is permitted to access personal data.
Equally important is the question of which data a particular operator does not need at all, and which information should remain difficult to access even if that operator’s account is compromised.
This is one of QEI’s core research directions.
“True trust in digital identity does not begin with the unlimited power of an administrator, but with a system that also places appropriate limits on that power.”
— Institute 1 April